Security
Your lead data, protected by design
Anviom CRM is built with access control, accountability and data isolation at its core. Here's how we protect your organization's data.
How we protect you
Security built into every layer
Every statement on this page reflects how the product works today.
Account & sign-in security
- Passwords are stored as salted bcrypt hashes — never in plain text.
- Short-lived access tokens (30 minutes) with refresh tokens that expire after 7 days.
- Per-device sessions: users can see where they're signed in and sign out other devices.
- Sign-in and password-reset endpoints are rate-limited per IP address.
- A password-expiry policy that prompts users to change their passwords regularly.
Data isolation & access control
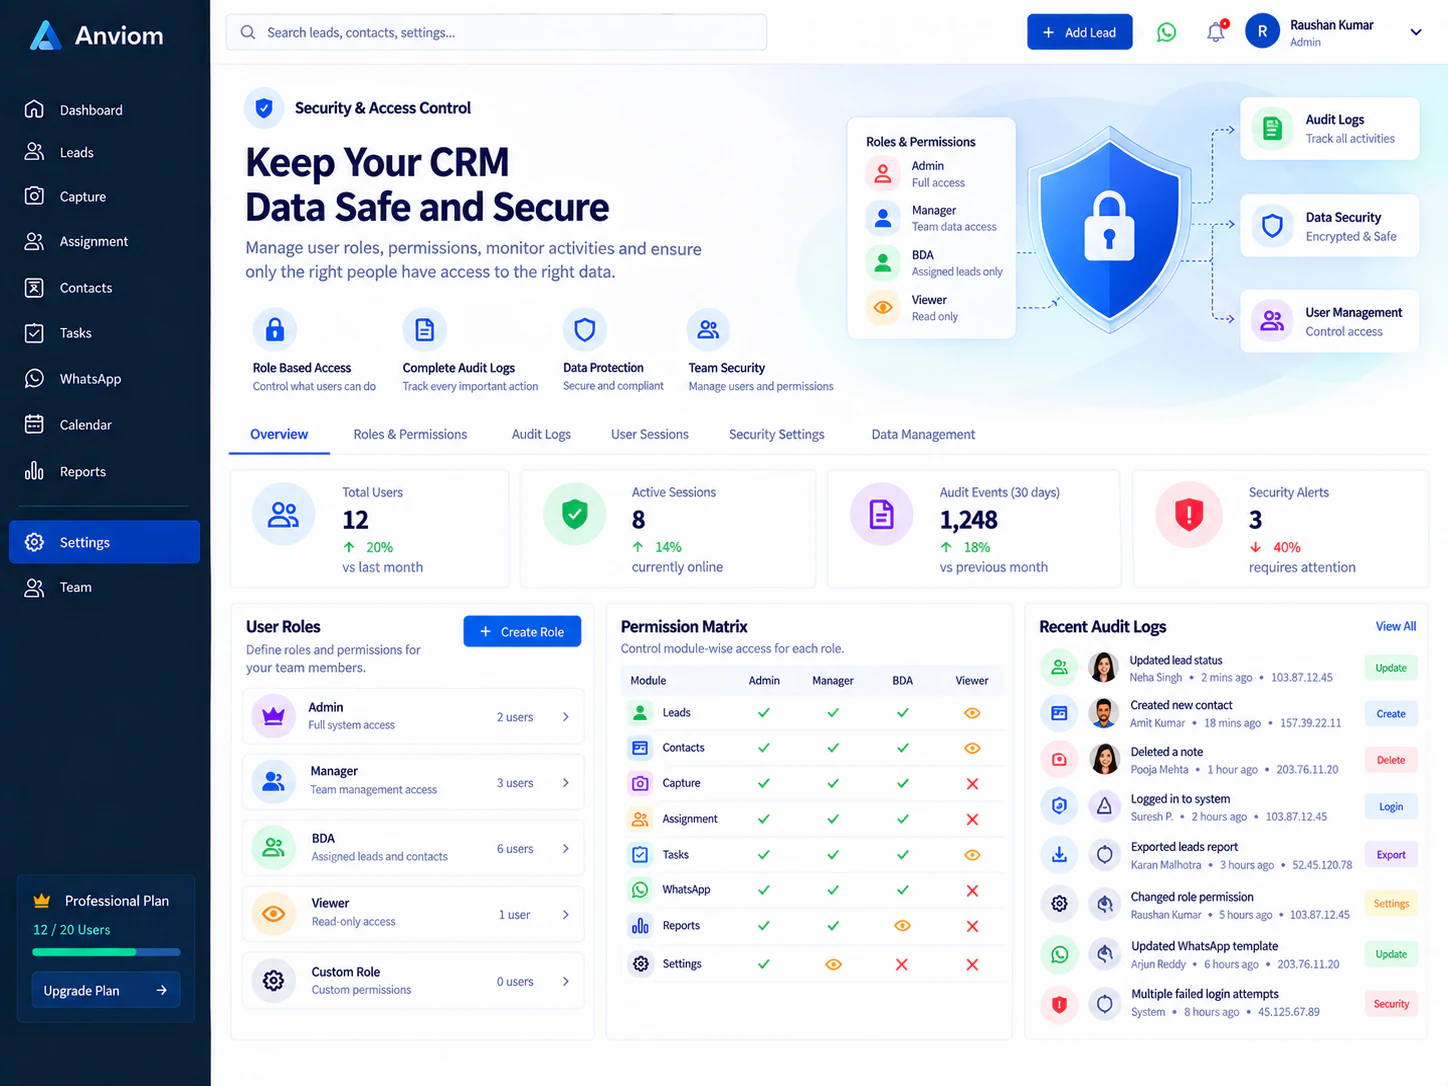
- Every record belongs to an organization, and requests are checked against the signed-in user's organization.
- Role hierarchy with visibility scopes — users see only their own, team, department, reporting-chain or organization-wide leads, as configured.
- Granular permissions per role, with per-user permission roles for exceptions.
- All customer data is stored in India, in the Amazon Web Services (AWS) Asia Pacific (Mumbai) region.
- Enterprise plans can run on a dedicated database.
Accountability
- An append-only audit log of significant actions, visible to administrators and exportable to CSV.
- Optional approvals for sensitive lead status changes.
- Every change to a lead is recorded in its timeline.
Payments
- Payments are processed by Razorpay. Card and bank details are entered in Razorpay's checkout and are not stored by Anviom.
Integrations
- Meta lead-ad and WhatsApp Business connections are authorised through Meta's own sign-in flow by your administrator.
- WhatsApp messages are sent through your organization's own WhatsApp Business account.
Data lifecycle
- When a subscription is cancelled, the organization's lead data is permanently deleted 30 days after cancellation.
- Billing and payment records are retained as required for financial compliance.
Infrastructure
- Hosting provider & region
- Amazon Web Services (AWS) — Asia Pacific (Mumbai) region, ap-south-1, India. All customer data is stored in India.
- Encryption in transit
- All communication between users and Anviom CRM is protected using HTTPS/TLS encryption. Database connections are also configured to use encrypted connections where supported.
- Encryption at rest
- Anviom customer data stored in the AWS database is protected using encryption at rest provided by AWS, subject to the configured database/storage encryption settings.
- Backups
- Database backups are maintained using AWS backup capabilities to support recovery in the event of accidental data deletion, database failure, or infrastructure issues.FrequencyDaily automated backupsRetention7 days
Service providers that process data for us are listed on our subprocessors page.
Report a security issue
If you believe you've found a security vulnerability, please report it privately to support@anviom.com. Please don't disclose it publicly until we've had a chance to respond.
Questions about security?
We're happy to walk your team through how Anviom CRM handles your data.